Application Security Management
The Atatus APM agents for Node.js, Python and PHP report the libraries your services load. Atatus flags the vulnerable versions, shows which services run them and names the version that fixes each CVE.
One risky library. Every service that runs it.
Click a library to light up the services that load it. Click a service to see its libraries.
Upgrade it. Watch it close.
Move to a newer version and see which CVEs it fixes. Fixed findings move from Open to Auto-Closed.
"mongoose": "4.0.1"Open 3
- Critical9.8
CVE-2022-2564fixed in 6.4.6 - Critical9.8
CVE-2022-24304fixed in 6.4.6 - Critical9.8
CVE-2023-3696fixed in 7.3.3
Auto-Closed 0
Move the slider to upgrade
Every library, with its license.

Detected by the APM agent for Node.js 3.1.0+Python 1.6.0+PHP 1.17.0+ · Composer
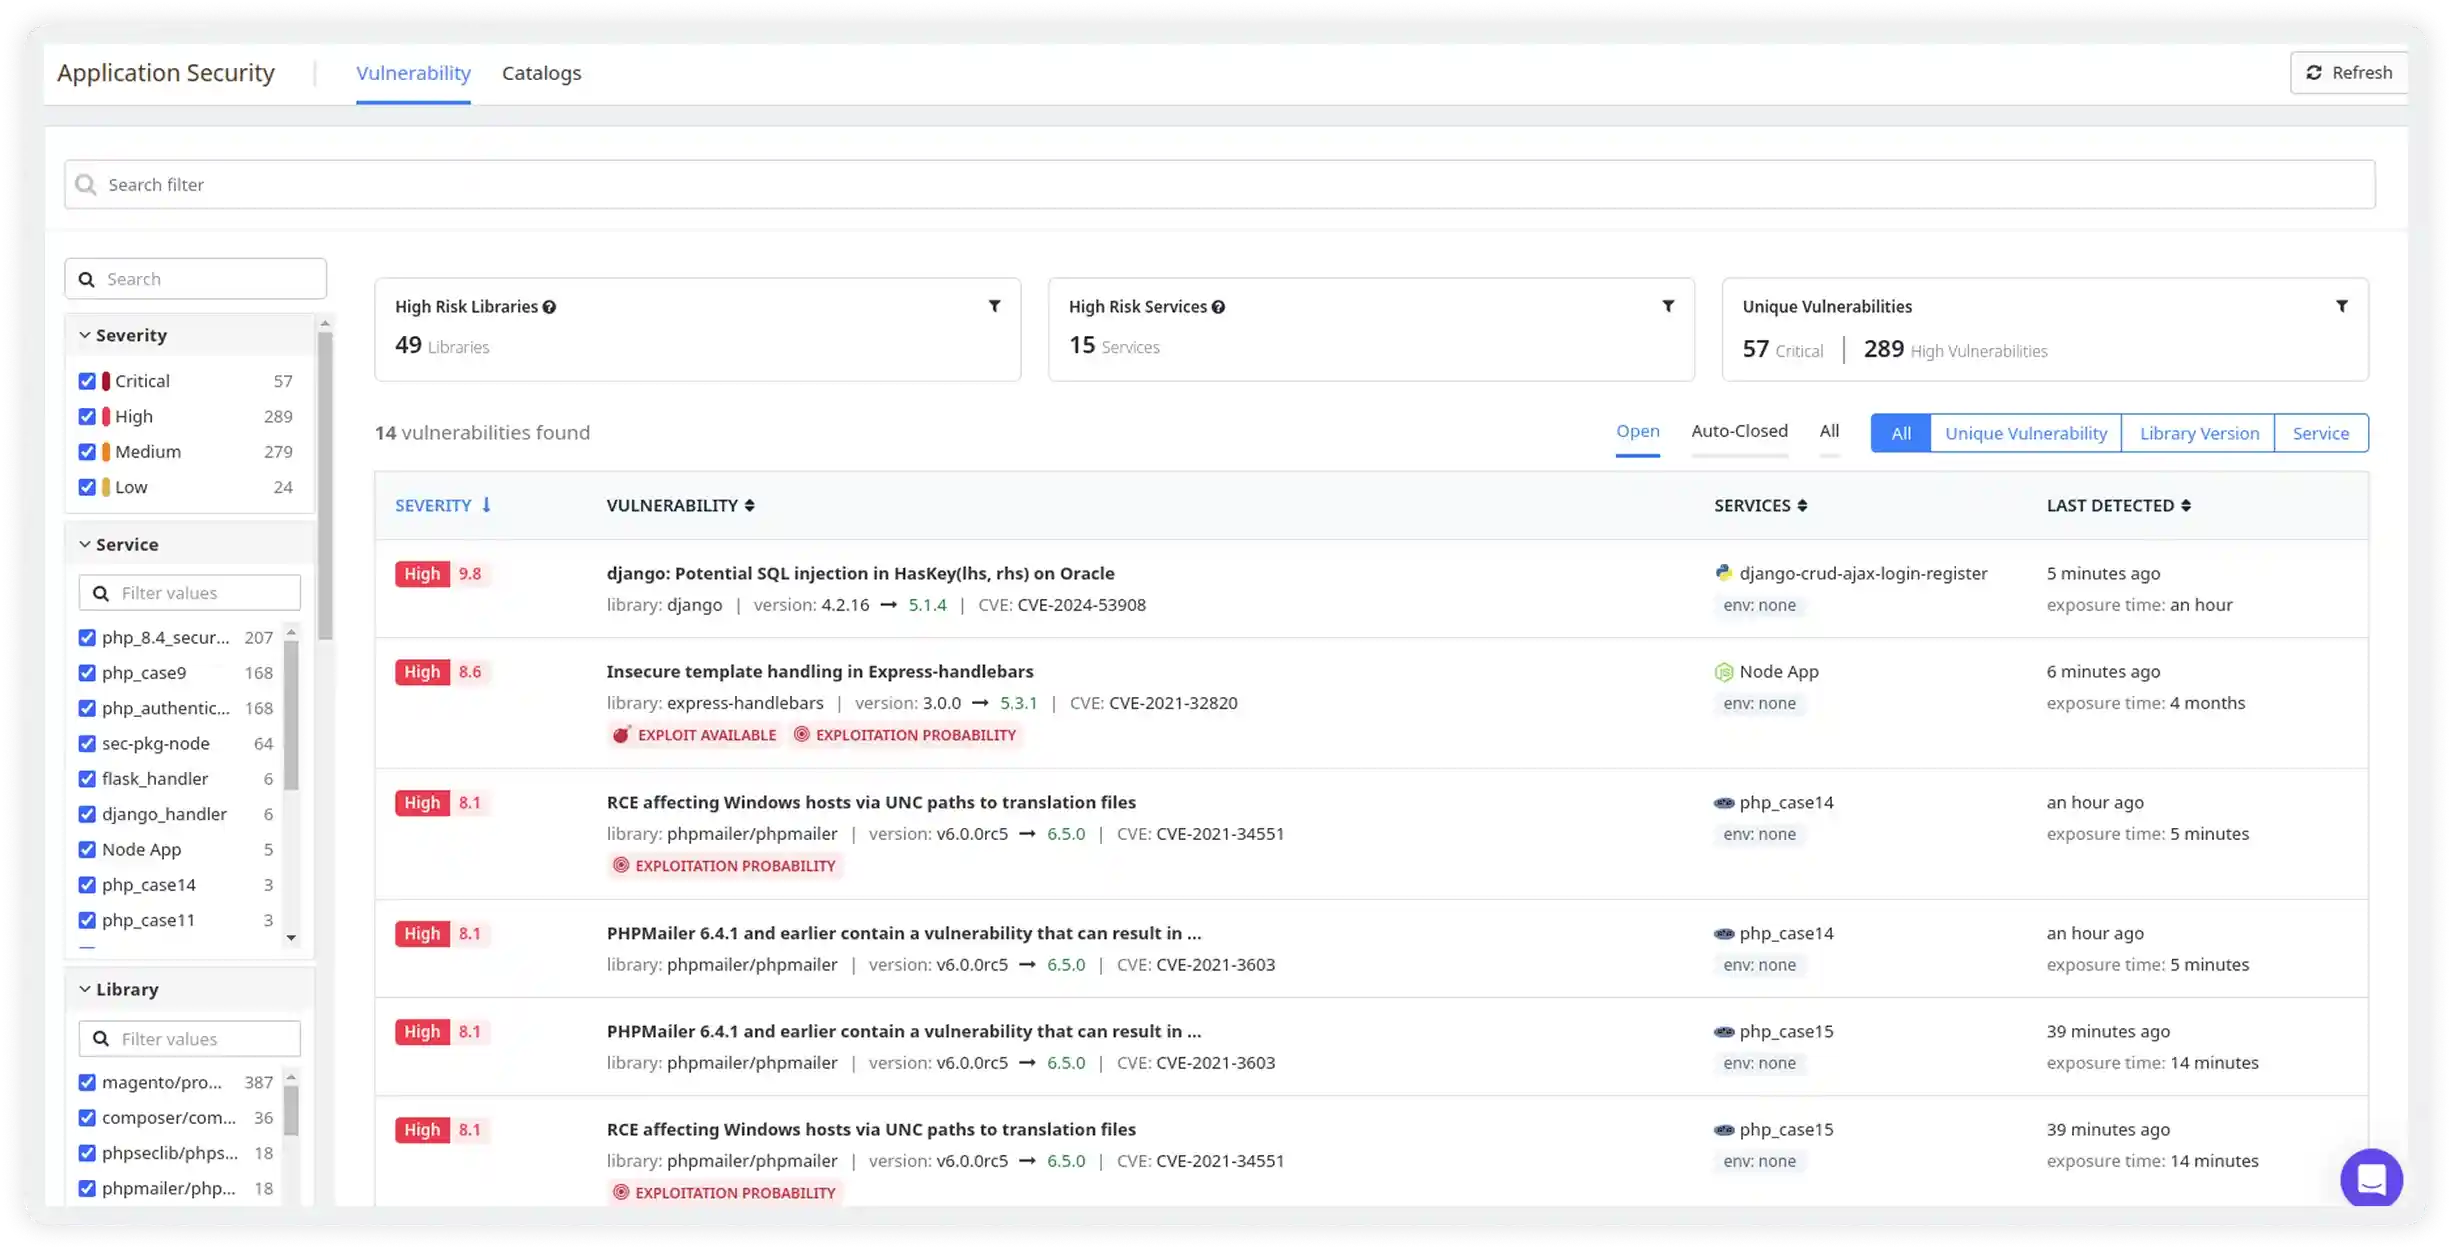
Application Security, screen by screen.
Real screens from the Atatus app.

Powering better performance for modern teams
"Solid Product even better support." The integration path is incredibly simple/easy and the overall interface is very intuitive. That said, I had a handful of odd use cases that the support team was incredibly responsive in helping me work through.
Questions about application security
Pricing, deployment, data and the agent. If something is missing, a person will answer it on a demo call.
In Atatus, application security finds vulnerable open source libraries in your running services. The APM agents for Node.js, Python and PHP report the libraries each service loads, and Atatus matches their versions to known CVEs and shows the version that fixes each one.
Node.js with agent 3.1.0 or later, Python with agent 1.6.0 or later, and PHP with Composer packages with agent 1.17.0 or later. Detection comes from the APM agent you already run in each service.
Many scanners check code or manifest files before you deploy. Atatus reads the libraries your services actually load through the APM agent, so each finding names the service and the environment that runs the vulnerable version.
Yes. The library catalog lists every library your services load with its version, its license, such as MIT or Apache-2.0, a Latest badge for up-to-date versions, its unique vulnerabilities and the services that use it.
Each finding shows its remediation, the version to upgrade to, for example upgrade cookie to 0.7.0. The Library Version view shows the recommended version for each library, and findings are split into Open and Auto-Closed tabs.
The overview shows high risk libraries, high risk services and unique vulnerabilities by severity. You can filter by severity, service, library and language, and group findings by unique vulnerability, library version or service. Each finding shows its CVE, EPSS score, first and last detected time and window of exposure.