Security teams can now detect threats, triage them and prepare for audits in the same platform as their APM and logs. Atatus Cloud SIEM (Security Information and Event Management) collects security events from your hosts, Kubernetes clusters, cloud accounts and identity tools and runs detection rules over them.
Every rule match becomes a signal with a severity, a risk score and its MITRE ATT&CK tactic and technique, so analysts can investigate and respond before an event turns into an incident.
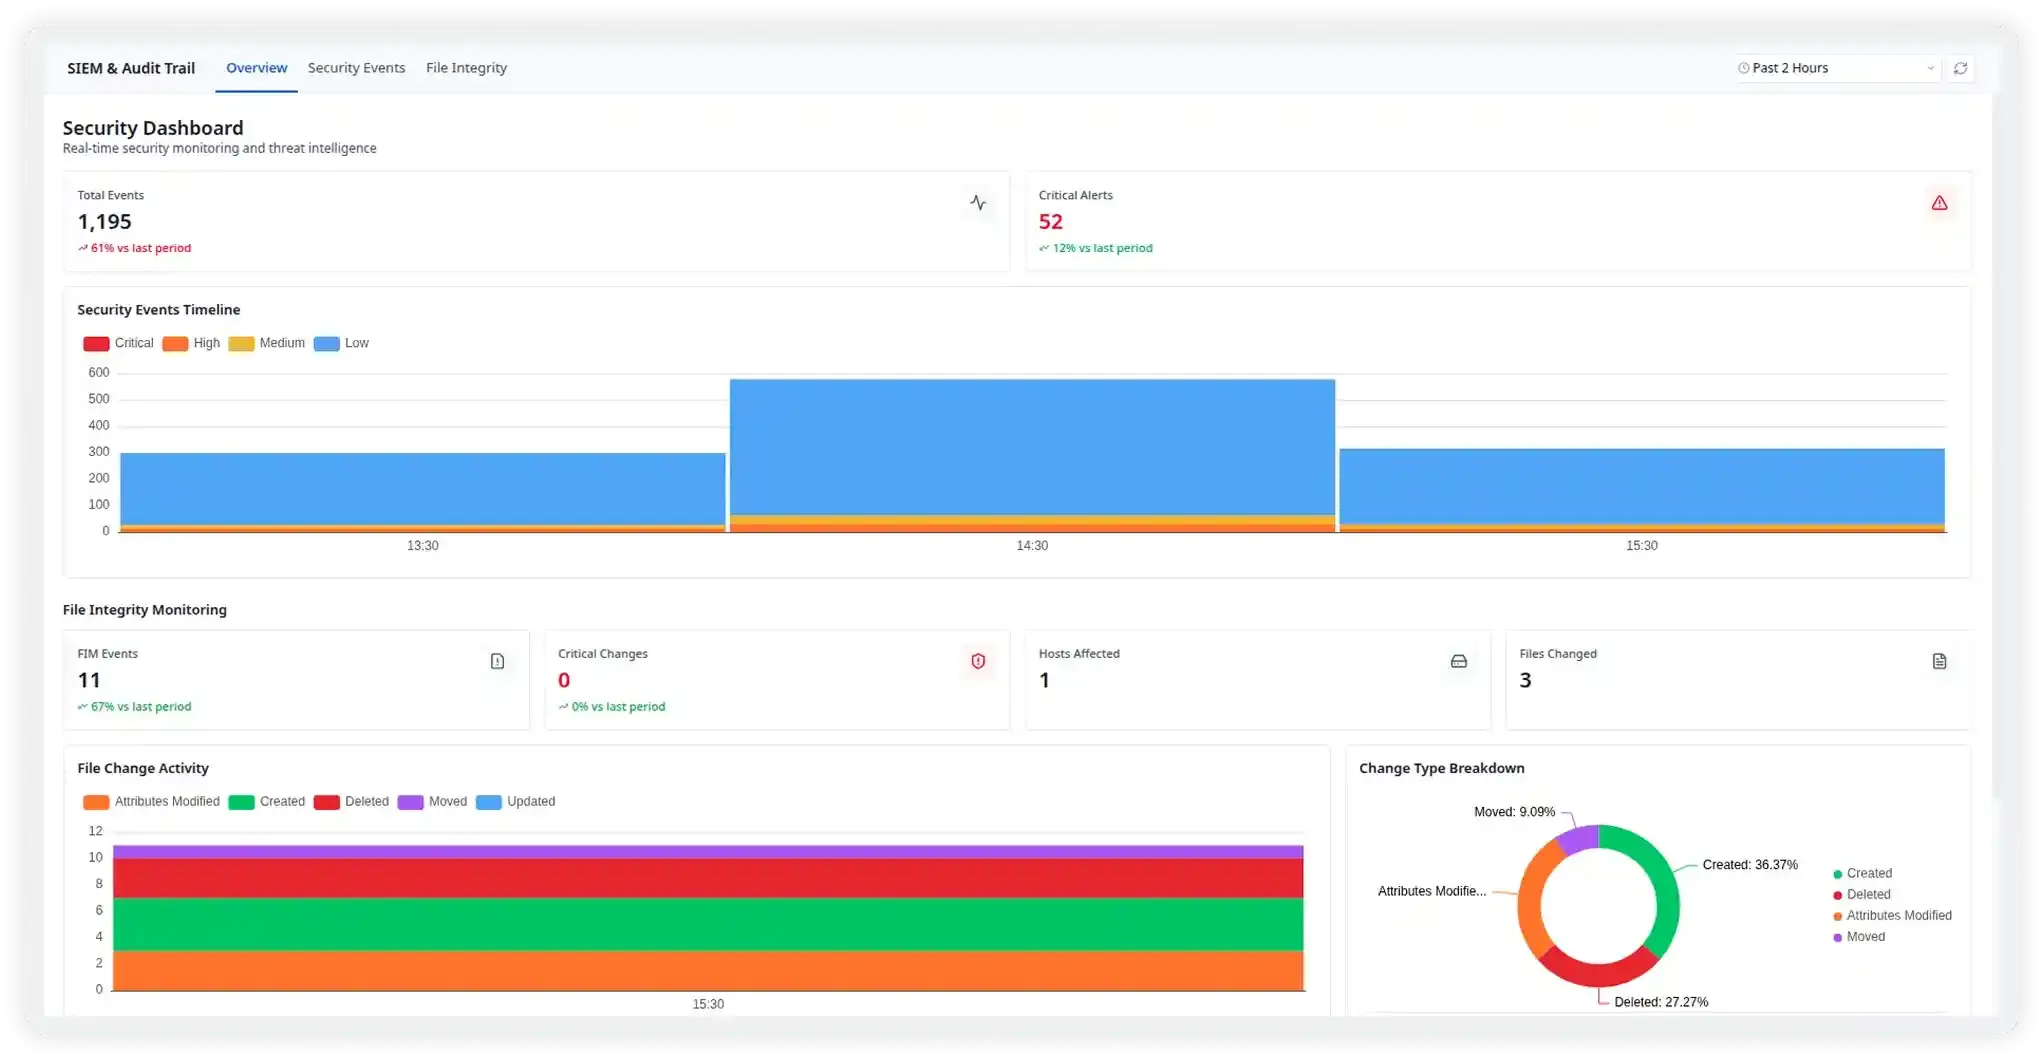
What Cloud SIEM gives you
- Threat detection: A built-in detection library, maintained by Atatus and mapped to MITRE ATT&CK, flags suspicious activity and known attack patterns across ingested events.
- One schema for every source: Events from identity providers, cloud accounts, firewalls and hosts are mapped to the same fields, such as user, source IP and outcome, so one search covers all of them.
- Custom detection rules: Build rules from queries, cases, notifications and suppressions, test them against recent data, or clone a built-in rule and edit it.
- Signal triage: Open a signal to see the matched events and the affected hosts, users and IPs, then assign it, change its status or suppress it. Repeated fires of a rule are grouped so you triage them once.
- Alerts where your team works: Send signals to Slack, Microsoft Teams, email or PagerDuty, with a different target for each severity.
- Compliance tracking: Track pass rates and control status for SOC 2, PCI DSS, HIPAA, ISO 27001, NIST 800-53, CIS Controls and GDPR on the Compliance tab.